


Cyber threats continue to intensify across the financial sector, with Registered Investment Advisors (RIAs) increasingly targeted due to the sensitive nature of the data they handle. These threats aren’t just growing in number—they’re becoming more sophisticated, requiring RIAs to adopt cybersecurity strategies that go beyond basic protections.
For RIAs registered with the SEC, cybersecurity isn’t optional. It’s a formal requirement. With tighter oversight from the Securities and Exchange Commission (SEC) and the Financial Industry Regulatory Authority (FINRA), firms must meet defined cybersecurity standards to ensure client protection and business integrity.
Cybersecureria was built with this exact challenge in mind—offering cybersecurity solutions designed specifically for RIAs. Its services not only meet regulatory standards but also help firms operate more securely as they grow.
Why Cybersecurity Compliance Is Critical for RIAs
The SEC and FINRA continue to elevate cybersecurity as a top compliance issue. The SEC’s Division of Examinations frequently releases risk alerts, and its 2024 Proposed Cybersecurity Rule outlines firm requirements for breach response, threat monitoring, and risk assessments.

Non-compliance carries real consequences:
- Legal action including fines, enforcement measures, and potentially even loss of registration.
- Operational disruption caused by attacks like ransomware, fraud, or prolonged downtime.
- Reputational harm leading to client dissatisfaction and attrition.
Recent examples prove the stakes:
- In 2023, a small advisory firm experienced a major data breach due to outdated systems, triggering regulatory action and a class-action lawsuit.
- A phishing scheme at a mid-tier RIA compromised clients’ personal data, resulting in both regulatory penalties and a loss of client confidence.
These incidents illustrate how cybersecurity gaps can quickly escalate into business-altering events. Compliance is no longer about checking boxes—it’s about protecting the future of your firm.
What Cybersecureria Brings to RIAs
Cybersecureria is a purpose-built cybersecurity service provider for RIAs. Unlike generic IT vendors, it specializes in helping financial advisors stay secure while meeting SEC and FINRA obligations.
Core services include:
- Tailored cybersecurity programs that map directly to current regulatory guidance.
- Ongoing compliance monitoring and preparation for audits and exams.
- Thorough risk assessments to uncover firm-specific vulnerabilities.
- Incident response planning with live exercises and breach simulations.
- Employee training programs to improve digital hygiene and reduce human error.
Cybersecureria’s expertise in the advisory space ensures that security programs are both effective and practical, never obstructing day-to-day business.
Key Features and Strategic Benefits
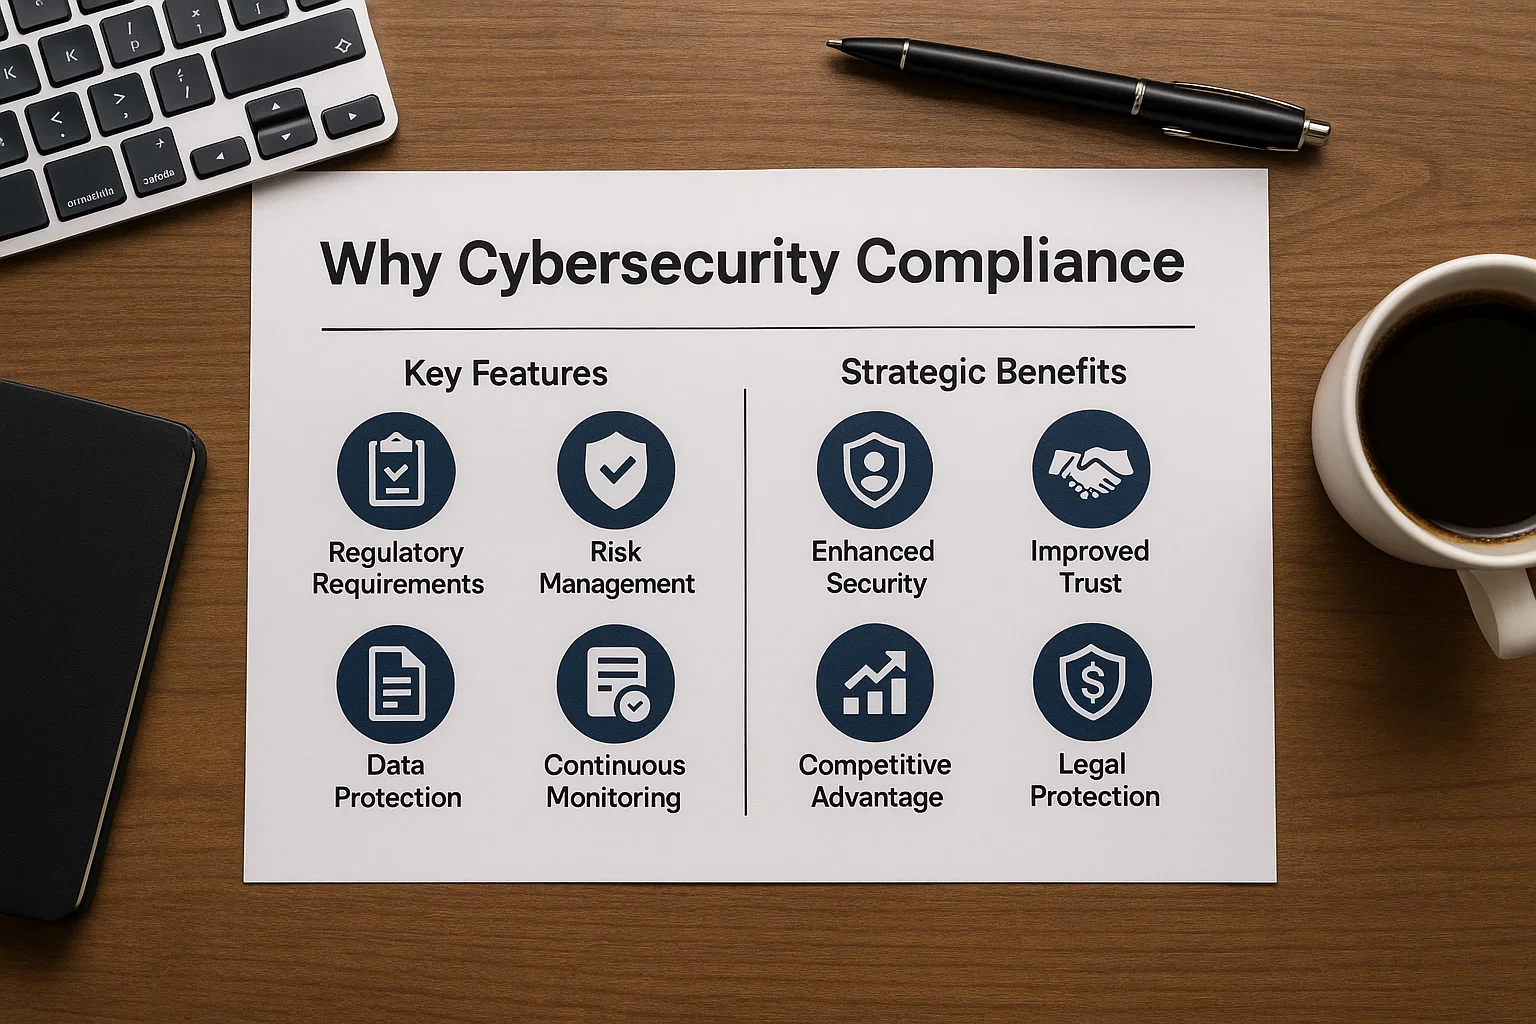
Cybersecureria’s solutions are built to be both powerful and easy to deploy. Firms benefit from:
Regulatory Readiness
Solutions are aligned with the SEC’s cybersecurity requirements, including controls in the latest proposed rules.
Fast Deployment
Processes, documentation, and technical controls are rolled out quickly without disrupting workflows.
Adaptable Solutions
Cybersecurity tools and support scale alongside your firm—whether managing $50 million or $5 billion in client assets.
Core Benefits Include:
- Reduced exposure to cyber risks across systems and personnel
- Easier, more efficient compliance processes
- Better preparation for SEC examinations
- Increased client trust through demonstrable safeguards
Helping RIAs Build Credibility and Scale Securely
Modern cybersecurity is as much about growth as it is about defense. Cybersecureria helps RIAs stand out in a competitive marketplace by demonstrating a clear commitment to client protection.
With Cybersecureria, firms can:
- Show that client data is managed responsibly and securely
- Present a security-first approach as a competitive differentiator
- Protect intellectual property like proprietary investment strategies and planning models
Strong cybersecurity builds confidence—not just with regulators, but with clients who expect their advisors to take digital threats seriously.
Real Results from Cybersecureria’s Work
One RIA managing over $800 million partnered with Cybersecureria after discovering vulnerabilities in its email systems and access controls. The firm lacked a structured incident response process and had no consolidated documentation of its cybersecurity measures.
In just three months:
- Its cybersecurity rating jumped from C+ to A on a recognized industry scale
- A mock SEC audit conducted by Cybersecureria revealed no critical gaps
- Employee susceptibility to phishing dropped from 28% to under 5% following targeted training
The firm’s CCO stated: “Cybersecureria made security measurable and compliance achievable. We now face regulators and clients with confidence.”
Getting Started: A Simple, Focused Approach
Cybersecureria’s onboarding process is designed for minimal disruption and maximum alignment with your firm’s needs.
Here’s what to expect:
- Initial discovery to assess your risk landscape and compliance status
- A tailored roadmap that prioritizes urgent security needs and regulatory gaps
- Dedicated onboarding with specialists guiding every step of implementation
Clients also receive:
- A single, dedicated point of contact for support and questions
- Regular updates and training materials for staff
- Thorough documentation to support SEC audits and reviews
Conclusion
For SEC-registered RIAs, cybersecurity and compliance are deeply interconnected. Cybersecureria stands out as a specialized partner that understands this balance. With deep regulatory expertise, flexible solutions, and a commitment to operational support, Cybersecureria enables RIAs to protect what matters most—their clients, their data, and their reputation.
To start building a more secure and compliant advisory firm, visit https://www.cybersecureria.com.